Governance & operability
Audit the controls—not just the decisions they produce.
When someone challenges an outcome, the question may be who changed the policy, not simply what score the event received.
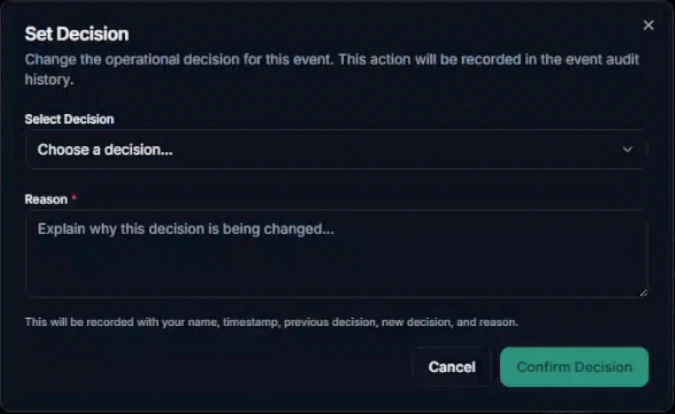
SENTR records configuration changes with user attribution and timestamps, including rules, policies, lists and reason codes. Decision explanations and reasoned overrides keep system findings and human judgement distinguishable.
Go deeper: Governance & operability
- Query the operational trail
- Audit logs are a report data source alongside events, rules, cases, profiles and integrations. Review changes and export evidence without treating the audit trail as a separate support request.
- Operate access and delivery
- Organisation and team settings, access policies, scoped API credentials and webhook delivery traces support the people running the deployment. Confirm authentication and data-handling requirements during technical and security review.
- Keep enforcement explicit
- SENTR returns the decision. Your connected application enforces the business response; configured webhooks handle downstream effects. Qualified Shadow Mode keeps SENTR out of production enforcement.
Give operators, engineering and governance a shared evidence trail. Security commitments are deployment-specific; SENTR does not claim certifications it does not hold.